Trust center
Trust and data protection in Caire
Where your data is stored, who can access it, how AI is used and which suppliers process data on our behalf.
- Planning data is stored in the AWS Stockholm region.
- AI features for signed-in users run in Azure Sweden Central.
- Your data trains no generative models.
- Every subprocessor is named in the DPA.
Overview
- Your organisation is the controller for data about employees, clients, schedules and visits. Caire (EirTech AB) is the processor.
- An organisation administrator accepts the data processing agreement (DPA) before any personal data can be added.
- The planner reviews and approves before anything is published.
Where data is stored
- Caire's production environment runs in the AWS eu-north-1 region in Stockholm. Planning data, backups and logs are stored there.
- Sign-in and accounts are handled by Clerk in the US. A few other suppliers process limited data outside the EU. The subprocessor table shows which.
- Data is not transferred outside the EU/EEA without your written permission and a valid GDPR transfer mechanism.
Access and sign-in
- Every request to the product needs a verified sign-in. An organisation administrator invites colleagues and gives them roles.
- Each organisation's data is kept apart, both in the permission checks and in the database's row-level security.
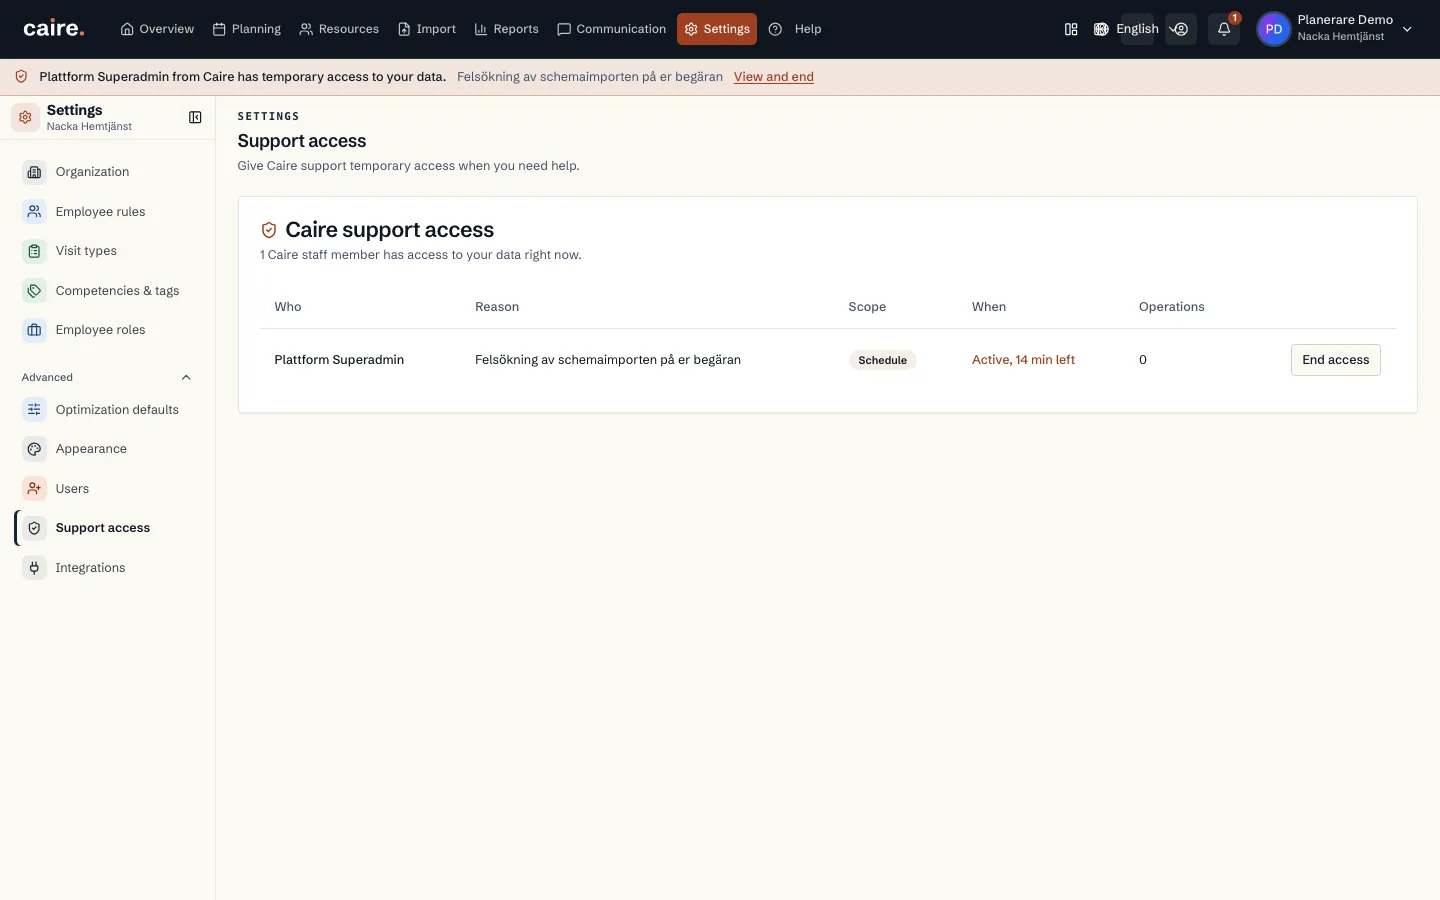
- Caire has no standing access to your data. Support access needs a stated reason, is time-limited and is logged. An organisation administrator sees current access and can end it.
- Caire's own staff sign in with two factors. Without the second factor, access is refused.
Encryption
- All traffic to the web app, the API and the mobile app is encrypted with TLS.
- The database and its backups are encrypted at rest, with keys in AWS KMS. Backups are taken automatically.
- Integration credentials are encrypted in the application with AES-256-GCM.
Sensitive data
- Every sensitive field has a class: personal data, health, note, salary, financial or care instruction. The class decides who may read the field.
- Personal identity numbers are shown only to users with a specific permission in their own organisation.
- For clients with protected identity, name, address and contact details are hidden from users without permission. The identity is never sent to the AI features.
- The planning assistant never receives identity numbers, health data, notes or salary data, whatever the user's permissions.
- Route optimisation receives pseudonymous identifiers and never the names of clients or employees.
- AI features in the product for signed-in users start only when an authorised user chooses them, and run in Azure Sweden Central. If that service does not respond, the request stops. There is no fallback outside the EU.
- Your data is not used to train generative models or to improve the service for other customers.
Logging and traceability
- Every read of health data is logged: who read it, which field and when.
- Support access, changed integration keys and changed settings are kept in audit logs that users cannot edit.
- Proposals and approvals are kept in a hash-chained decision log.
- Sign-ins and failed sign-ins are recorded.
- Log extracts for your organisation are provided on request.
- Changes reach production through reviewed and logged workflows, and a release can be rolled back.
Subprocessors
- We inform you before a new subprocessor starts processing your personal data, and you can object on reasonable grounds. The transfer safeguard for each supplier is in DPA appendix 1.
- The optimisation engine is exchangeable. Caire connects the engine through its own provider-neutral interface and calculates the figures itself, so the engine can be replaced by another or run in-house. The Timefold solver core is open source.
| Subprocessor | Purpose | Where |
|---|---|---|
| Amazon Web Services EMEA SARL | Hosting and storage of the service, including backups and logs | Stockholm (AWS eu-north-1) |
| Microsoft Azure, inklusive Azure OpenAI | AI features started by an authorised user | Sweden (Azure Sweden Central) |
| Timefold BV | Route and schedule optimisation with pseudonymised data | EU/EEA |
| Clerk, Inc. | Sign-in, organisations, roles and invitations | United States |
| Stripe Payments Europe, Limited | Subscriptions and billing, the organisation's billing details only | Ireland, United States and other countries |
| Resend (Plus Five Five, Inc.) | Email from Caire, without care documentation | United States |
| Expo (650 Industries, Inc.) | Push notifications to the mobile app, without names, addresses or care data | United States |
| Sentry (Functional Software, Inc.) | Error and performance monitoring, with events designed to carry no personal data | EU (Frankfurt) for events, United States for account data |
| Mapbox, Inc. | Maps, route lines and address lookup | United States |
Data processing agreement
- The agreement is versioned, and Caire records which version your organisation accepted. The current version is open for anyone to read.
- You can audit our compliance once per twelve-month period, and more often if you suspect a breach.
- When processing ends, we return or delete the data as you choose, no later than 30 days after the agreement ends. The deletion is confirmed in writing.
- An authorised representative requests return or deletion through info@caire.se, without sensitive attachments.
Requests for return or deletion: info@caire.se
Incidents and contact
- A suspected security event is confirmed and investigated within one hour.
- If a personal data breach occurs, we notify you without undue delay, with a target of 12 hours. You get the facts you need for your own report to the supervisory authority.
Security questions or a suspected incident: support@caire.se
Integrations
- Integration API keys require an accepted DPA before personal data may be imported.
How Caire connects to other systems is described in the Caire Connect help article.
Availability
- Service levels, support and incident handling are set out in the customer agreement.
Documents
Open the documents directly, or request what applies to your organisation.
- Data processing agreement (DPA)Open
- Privacy policyOpen
- Terms of serviceOpen
- Security, sign-in and the DPA (help article)Open
- Security log extracts for your organisationRequest
- Answers to security questions for a tenderRequest
Security questions or a suspected incident: support@caire.se